The CISSP Mindset: Mastering the 8 Domains of Cybersecurity Leadership
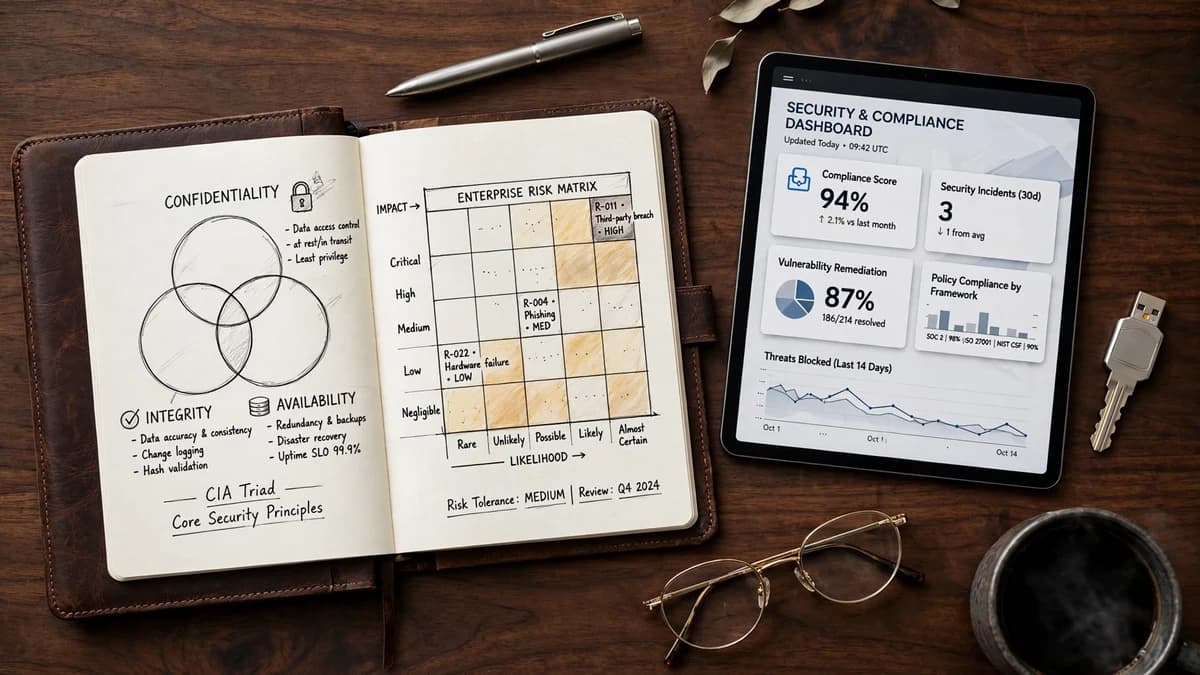
The Certified Information Systems Security Professional (CISSP) credential, governed by ISC2, is widely regarded as the crown jewel of the cybersecurity industry. It is the defining standard for senior security professionals, chief information security officers (CISOs), and enterprise architects. However, unlike highly technical certifications that test your ability to configure a firewall or execute a penetration test, the CISSP tests your ability to protect the entire organization from a strategic, risk-based perspective.
Earning the CISSP designation proves that you possess the broad technical knowledge and executive leadership skills required to design, engineer, implement, and manage an organization's overall security posture. As cyber threats become more sophisticated and regulatory environments grow increasingly complex, the demand for professionals who can bridge the gap between technical execution and business strategy has never been higher.
This guide provides a definitive blueprint for the modern CISSP exam. We will deconstruct the critical "Think Like a Manager" mindset, break down the updated weighting of the 8 core domains, and establish a high-performance preparation strategy to ensure your success on exam day.
The CISSP Paradox: The "Think Like a Manager" Mindset
The single greatest hurdle for candidates taking the CISSP exam is their own technical expertise. Engineers, analysts, and administrators spend their careers finding immediate, technical solutions to operational problems. If a server is vulnerable, they patch it. If a network segment is compromised, they isolate it.
To pass the CISSP, you must actively unlearn this instinct. The CISSP is fundamentally a management and risk exam. It demands that you view every scenario through the lens of human safety, legal liability, and business continuity.
When presented with a scenario on the exam, you must adopt the "Think Like a Manager" mindset. This requires adhering to several core axioms:
- Human safety is always the primary concern. If a question involves a fire in a data center, the correct answer is always to evacuate personnel, regardless of the data processing taking place.
- Do not fix the problem; fix the process. A manager does not apply a technical patch; a manager investigates why the patch management policy failed and implements a new governance control.
- Risk dictates action. Security is never absolute. The goal of information security is not to eliminate all risk, but to reduce risk to an acceptable level as defined by senior management. Controls should never cost more to implement than the value of the asset they are protecting.
- You advise; senior management decides. As a security professional, your role is to perform risk assessments, calculate potential impact, and present options. Final accountability and acceptance of risk always lie with executive leadership.
Exam Architecture & Logistics
Before committing to your preparation, it is crucial to understand the stringent requirements and the structural mechanics of the exam.
- Experience Prerequisites: To earn the CISSP, you must possess a minimum of five years of cumulative, paid, full-time work experience in two or more of the eight domains of the CISSP Common Body of Knowledge (CBK). A four-year college degree or an approved credential (such as CompTIA Security+) can satisfy one year of the required experience.
- Computerized Adaptive Testing (CAT): The English version of the CISSP exam uses adaptive testing technology. The difficulty of the questions adjusts based on your previous answers.
- Length and Time: The exam consists of a minimum of 100 questions and a maximum of 150 questions. You are given a maximum of three hours to complete the test.
- Endorsement: Passing the exam is only the first step. You must subsequently be endorsed by another active ISC2 certified professional who can attest to your professional experience.
Evaluate your readiness with our free CISSP diagnostic exam on CertFactory
Deconstructing the 8 Domains of the CISSP
ISC2 regularly updates the CISSP Detailed Content Outline following a Job Task Analysis to ensure the exam reflects the realities of the modern threat landscape. The most recent structural update went into effect on April 15, 2024, resulting in minor adjustments to the exam weights.
To succeed, you must demonstrate competence across all eight of the following domains.
Domain 1: Security and Risk Management (16%)
As of the April 2024 update, this is the most heavily weighted domain on the exam, increasing to 16%. This reflects the industry's overriding focus on governance and risk. This domain establishes the foundational principles of information security: the CIA Triad (Confidentiality, Integrity, and Availability). You must understand how to align security functions with business strategy. You will be tested on risk management frameworks, legal and regulatory compliance (such as GDPR), threat modeling methodologies, and the creation of security policies, standards, procedures, and guidelines. Furthermore, this domain covers personnel security, including candidate screening, onboarding, and termination processes.
Domain 2: Asset Security (10%)
This domain focuses on the protection, handling, and lifecycle of the organization's information assets. While it carries the lowest weight on the exam (10%), it is foundational to all other domains—you cannot protect what you have not identified. Key topics include data classification schemes, establishing data ownership, and managing the entire data lifecycle. You must understand asset retention policies, end-of-life (EoL) destruction processes, and the implementation of robust data security controls.
Domain 3: Security Architecture and Engineering (13%)
This highly technical domain bridges the gap between theoretical security models and practical system implementation. Accounting for 13% of the exam, it requires a deep understanding of how to build systems securely from the ground up. You will be evaluated on fundamental security models (such as Bell-LaPadula and Biba), secure design principles, and assessing vulnerabilities in distributed systems. A massive component of this domain is cryptography; you must possess a solid grasp of symmetric and asymmetric encryption, hashing algorithms, Public Key Infrastructure (PKI), and methods of cryptanalytic attacks.
Domain 4: Communication and Network Security (13%)
Representing 13% of the exam, this domain covers the design and protection of network infrastructures. It is one of the more challenging sections for candidates who lack a strong networking background. You must demonstrate fluency in the OSI and TCP/IP models, understanding exactly which protocols operate at each layer. Topics include securing network components (routers, switches, firewalls), designing secure communication channels (VPNs, IPsec, TLS), and mitigating network-based attacks.
Domain 5: Identity and Access Management (IAM) (13%)
In a modern perimeter-less, cloud-first environment, identity is the new security boundary. This domain (13%) focuses on controlling how users and devices are identified, authenticated, and authorized to access data. You will be tested on physical and logical access controls, the integration of Identity as a Service (IDaaS), and the implementation of multi-factor authentication (MFA) and biometric systems. Furthermore, you must understand the complete identity provisioning lifecycle and authorization mechanisms such as Role-Based Access Control (RBAC) and Attribute-Based Access Control (ABAC).
Domain 6: Security Assessment and Testing (12%)
Security controls are useless if they are not continuously validated. Comprising 12% of the exam, this domain focuses on the design, performance, and analysis of security testing. Expect detailed questions on vulnerability assessments, penetration testing methodologies, and the management of internal and third-party security audits. You must understand how to collect security process data and evaluate the outputs of tests to ensure controls are functioning as designed.
Domain 7: Security Operations (13%)
This domain (13%) represents the day-to-day tactical execution of security management. It is the domain most familiar to working SOC analysts and systems administrators. Key concepts include incident response handling, digital forensics, and managing logging and monitoring systems. Crucially, this domain also covers physical security (perimeter defenses, HVAC systems, fire suppression) and the execution of Disaster Recovery (DR) and Business Continuity (BC) plans. You must understand how to maintain operational resilience during a crisis.
Domain 8: Software Development Security (10%)
Following the April 2024 update, the weight of this domain was slightly decreased from 11% to 10%. It evaluates your ability to apply and enforce security principles throughout the Software Development Life Cycle (SDLC). You must understand the security implications of various development methodologies (Agile, Waterfall, DevSecOps), secure coding guidelines, and how to identify common software vulnerabilities (such as those outlined in the OWASP Top 10). The domain also covers the effectiveness of software security and controls within development ecosystems.
Strategic Preparation and Execution
The CISSP is often described as "a mile wide and an inch deep." The sheer volume of material is the primary challenge. To succeed, your study strategy must be as disciplined as your security policies.
- Establish a Baseline with Mock Exams: Do not wait until you have finished reading the Official Study Guide (OSG) to take a practice test. Take a full diagnostic exam on day one. This will immediately highlight your weakest domains, allowing you to allocate your study time efficiently.
- Focus on the "Why," Not Just the "What": Rote memorization of cryptographic key lengths will only get you so far. The adaptive exam tests application and analysis. When reviewing practice questions, focus heavily on the expert rationales. You must understand why the correct answer is the best managerial choice, and why the distractors are operationally inferior.
- Master the End-Game: In the final weeks of preparation, shift your focus entirely to scenario-based questions that force you to prioritize actions. When a question asks for the "first," "best," or "most important" step, immediately defer to human safety, local laws, and organizational policy.
The CISSP is a rigorous, demanding credential, but achieving it permanently alters the trajectory of your career. By mastering the 8 domains and embracing the mindset of a strategic leader, you will be well-equipped to conquer the exam and drive the future of enterprise cybersecurity.
Ready to test your knowledge?
Browse our full catalog of expert-crafted practice exams.